Short answer: Select a DDoS protection service after ranking which websites, APIs, DNS, VPN, email and network prefixes must remain available; baselining normal traffic and defining acceptable degraded service; mapping every DNS, BGP, GRE, proxy, CDN, origin and upstream route; restricting direct origin access; testing volumetric, protocol, reflection, connection and application-resource exhaustion with provider authorization; measuring detection and mitigation time, clean-traffic accuracy and geographic latency; verifying automatic versus on-demand activation and secure out-of-band controls; confirming provider capacity, upstream arrangements, regional resilience and service thresholds; preparing static or limited-function fallbacks; integrating telemetry, packet evidence, application health and cost alerts; exercising incident roles and secondary-attack monitoring; defining attack-period pricing and billing caps; and rehearsing routing withdrawal and migration. A large scrubbing number is not useful when a critical service, DNS path or origin remains outside protection.
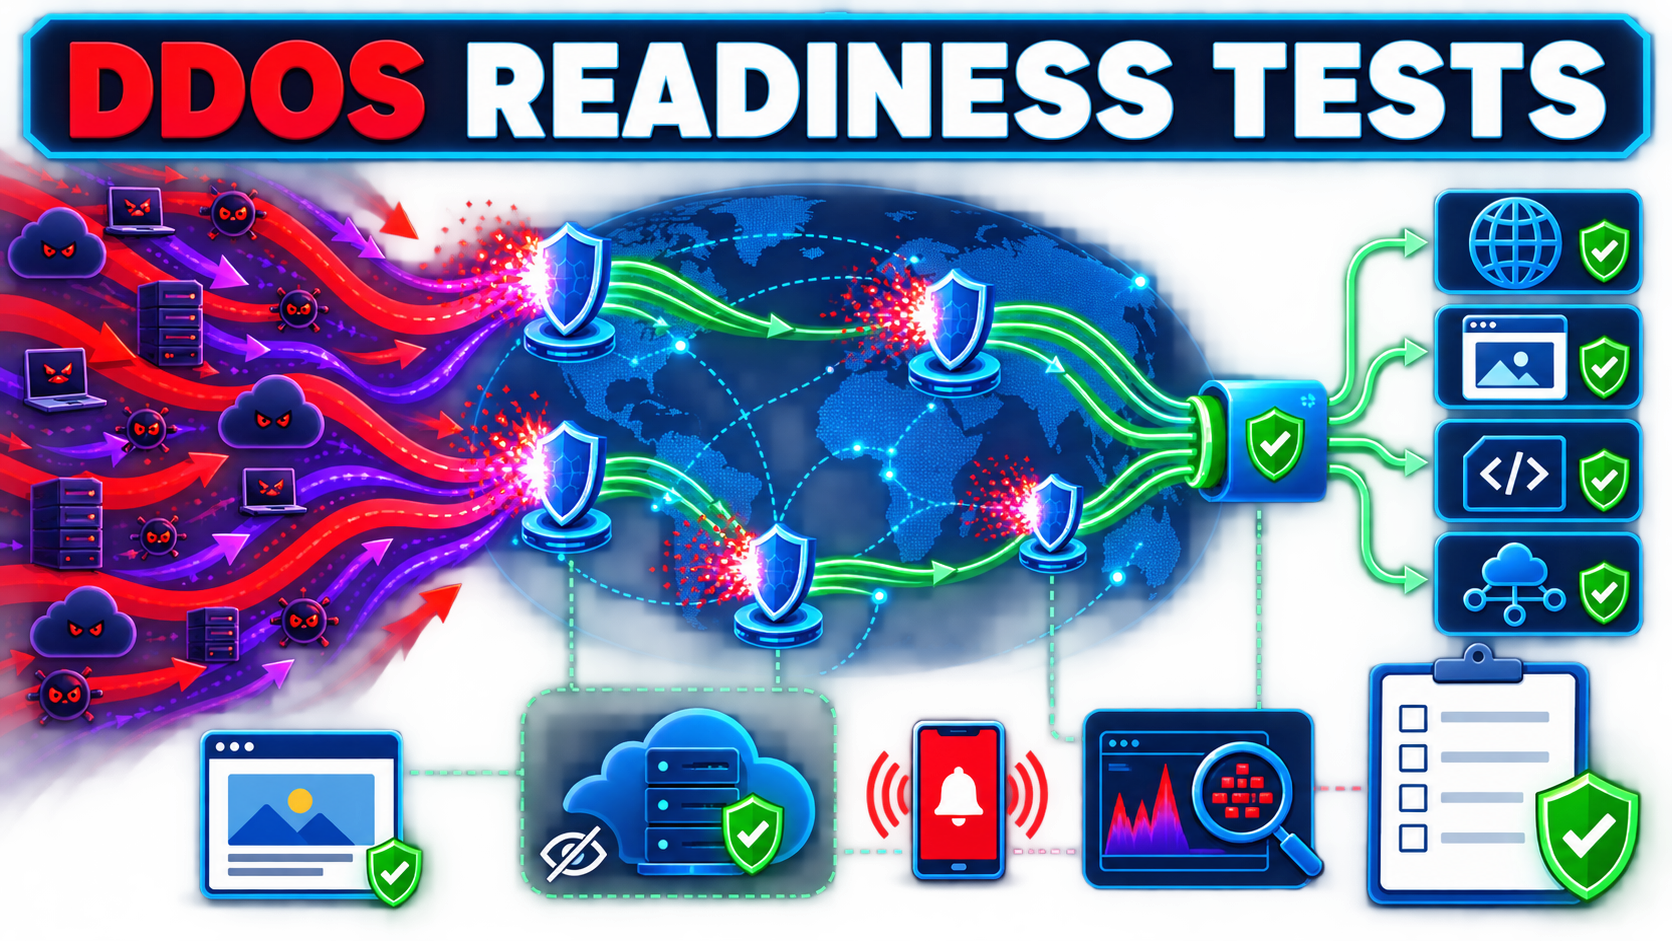
CISA recommends proactive risk assessment, monitoring, response plans and mitigation-provider preparation. Australia's ASD emphasizes that preparation before an attack is far more effective than improvised response and recommends protecting origins, defining acceptable service and discussing capacity, pricing and pre-approved actions with providers.
Normalize the same protected assets, protocols, peaks, attack vectors, regions, activation mode, legitimate-client distribution, response objectives, evidence, support and cost scenario. Always-on proxy, BGP diversion, CDN and on-demand scrubbing services have different detection, routing and latency behavior.
Prioritize Services And Degraded Modes
Inventory authoritative DNS, web, APIs, remote access, email, customer portals, network ranges and third-party dependencies. Assign availability objective, peak legitimate load, maximum outage and owner. Decide which functions can be disabled or served statically during an attack.
Baseline bandwidth, packets, connections, requests, compute, database and paid downstream actions. Application attacks may exhaust search, login, SMS, reports or database resources without filling the network link.
Trace Every Route And Hide Origins
Diagram DNS, CDN, proxy, BGP, GRE, load balancers, firewalls, cloud regions and upstream carriers in both normal and mitigation states. Include IPv6, non-web protocols and disaster-recovery addresses.
Restrict origins to scrubbing or authorized management networks where possible. Test historical DNS, certificate transparency, email headers, direct IP, alternate hostnames and adjacent subnets for leaks. A changed origin address needs a process to remain undisclosed.
Exercise Approved Attack And Failure Scenarios
With written provider and owner authorization, test representative volumetric, reflection, SYN or connection, TLS, HTTP and expensive-application requests. Measure detection, diversion, mitigation and recovery while verifying legitimate clients from multiple networks.
Fail an edge, tunnel, provider region, control plane and out-of-band communication path. Test automatic and manual activation, route convergence, stale DNS and rollback. Confirm no mitigation loops or unexpected blackholing.
Coordinate Evidence And Incident Response
Provide real-time service health, traffic, packet or flow evidence, mitigated vectors, false positives and cost. Correlate network traffic with server CPU, memory, database and application availability. Retain packet samples and decisions needed for review.
Exercise contacts, escalation, pre-approved changes, customer communication and business continuity. Continue monitoring other systems because DDoS can distract defenders from a separate intrusion. Document recovery criteria and post-incident tuning.
Bound Commercial Risk And Exit
Model clean traffic, attack traffic, bandwidth, requests, protected prefixes, tunnels, logs, premium response and surge charges. Confirm billing caps, attack credits, service limits and the conditions under which a provider may disable service.
Maintain portable DNS, routing, origin controls, certificates, allowlists and runbooks. Rehearse moving one service or prefix, withdrawing advertisements or proxy routes, and deleting provider credentials and retained traffic data.
Normalize DDoS Protection Evaluations
Normalize Exposure
Use One Asset Map
Compare identical DNS, hosts, APIs, prefixes, protocols, origins and dependencies.
Use One Baseline
Measure the same legitimate peaks, client geographies and resource bottlenecks.
Normalize Attacks
Use One Authorized Test
Run identical volume, protocol, connection and application exhaustion scenarios.
Use One Failure Set
Fail routing, tunnel, edge, region, control plane and communication paths.
Normalize Response
Use One Timeline
Measure detect, activate, mitigate, notify, recover and post-incident evidence.
Use One Cost Scenario
Price normal traffic, severe attack, logs, response and service thresholds.
DDoS Protection Service Scorecard
| Buying area | What to confirm | Why it matters |
|---|---|---|
| Assets | DNS, web, APIs, VPN, email, prefixes, dependencies | Prevents critical paths from remaining unprotected |
| Routing | Proxy, CDN, BGP, tunnels, IPv6, carriers, rollback | Determines how traffic reaches mitigation |
| Origin | Network restriction, IP leaks, alternate names, history | Stops direct attacks around protection |
| Attack coverage | Volume, reflection, protocol, connection, application | Covers different resource exhaustion modes |
| Activation | Automatic, on-demand, out-of-band, convergence, approvals | Controls time to effective mitigation |
| Resilience | Capacity, regions, upstreams, fallback, provider failure | Preserves service through large or compound events |
| Evidence | Health, traffic, vectors, packets, decisions, cost | Supports response and post-incident improvement |
| Commercial | Normal and attack pricing, caps, limits, credits, exit | Prevents an attack from creating unbounded cost |
Questions To Ask Before Shortlisting
- Which online services and network ranges must remain available?
- What degraded functionality is acceptable during an attack?
- Which DNS, IPv6, disaster-recovery or non-web paths are outside protection?
- Can attackers discover and reach the origin directly?
- Which volumetric, protocol and application attacks were authorized for testing?
- How long do detection, diversion and clean-traffic recovery take?
- What automatic actions and service cutoffs can the provider apply?
- What happens if a tunnel, region or control plane fails?
- Which out-of-band contacts and pre-approved changes exist?
- Can packet and decision evidence be exported in real time?
- How are other systems monitored during a distracting attack?
- What is the maximum attack-period cost and tested migration path?
Buying Red Flags
Capacity is advertised globally but no protected-asset, protocol or upstream map exists.
Origins remain publicly accessible or are easily found in historical records.
Testing is prohibited or limited to a dashboard simulation with no traffic path validation.
The provider can turn off service or create surge charges without clear thresholds and notification.
Incident response depends on ordinary email or portal access that may fail during the attack.
Source Links
- CISA: Understanding And Responding To DDoS Attacks
- CISA: UDP-Based Amplification Attacks
- ASD: Preparing For And Responding To Denial-Of-Service Attacks
- ASD: Guidelines For Networking
FAQ
What is the difference between DoS and DDoS?
A denial-of-service attack disrupts availability; a distributed attack uses many sources, often making filtering and capacity defense more difficult.
Is a CDN enough for DDoS protection?
It may absorb and cache substantial traffic, but buyers must verify DNS, origin isolation, protocols, application resources, capacity, response and bypass paths.
Why test application-layer exhaustion?
A modest request volume can trigger expensive search, login, report, database or paid-message work even when network bandwidth is not saturated.
Should protection be always on?
Always-on and on-demand models trade latency, cost and activation risk differently. The right choice depends on service objectives and tested routing behavior.
What is a static fallback?
It is a reduced site or service that uses minimal dynamic processing and bandwidth so essential information remains available during an attack.
Can DDoS be a distraction?
Yes. Defenders should continue monitoring other assets and authentication activity while mitigating the availability incident.
Related Software Buying Guides
- Web Application Firewall Software Buying Tests
- Network Monitoring Software Checklist
- Business Continuity Management Software Checklist
DDoS protection is readiness, not capacity marketing: every critical path must be covered, every route and fallback tested, every responder reachable, and every attack cost bounded before traffic arrives.