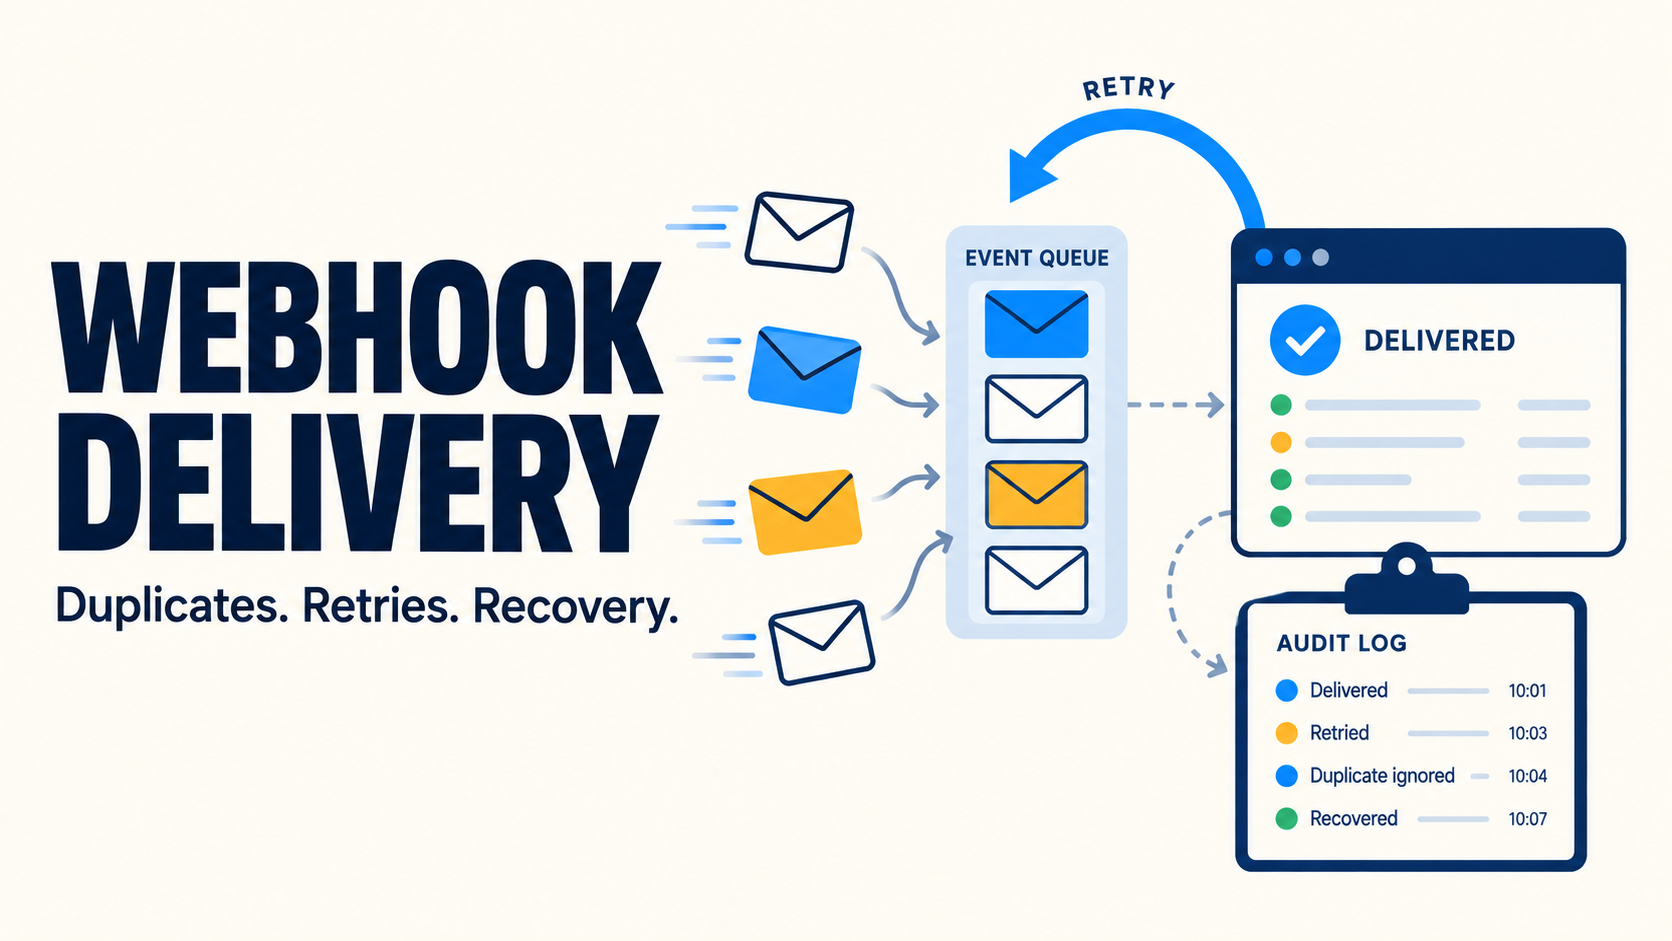
Buy a webhook delivery platform only after it demonstrates what happens to an event during duplicates, downtime, replay, and credential rotation. A dashboard full of successful requests does not prove that a business action happened once or that a failed delivery can be recovered safely. Evaluate the complete path from sender to durable business result.
The exercises below are proposed purchasing tests, not results from a hands-on product comparison. Run them in an authorized sandbox using synthetic records. The goal is to decide which responsibilities the platform takes over and which remain in your application.
Draw the acknowledgment boundary
Ask the vendor to draw where an incoming event is accepted, stored, forwarded, and marked complete. Identify exactly what a success response means at each boundary. A receiver may acknowledge durable receipt before a worker finishes the business action; that distinction needs to remain visible in support tools and service commitments.
GitHub’s webhook guidance recommends prompt responses and asynchronous processing where needed. That is a useful operational pattern, but buyers still need to ask what survives a worker crash after acknowledgment. Have the demonstration stop a worker at that point and show where the unprocessed event remains.
Define the evidence before the demonstration
Use one synthetic event identifier and record its delivery attempts, queue state, processing state, and final application outcome. Agree which timestamps and identifiers will be exportable. Without a shared evidence sheet, a vendor can demonstrate request success while your team is asking about business completion.
A practical acceptance statement
For a sandbox ticket-creation event, ask the team to show one intended ticket, a traceable record of every delivery attempt, and a recoverable explanation for any unfinished processing. This is a proposed outcome for the exercise, not a claim that every webhook provider guarantees exactly-once effects.
Separate duplicates from ordering
Stripe documents duplicate events and does not guarantee delivery order. Those are distinct application concerns. A platform that suppresses a repeated delivery identifier may still forward a different event concerning the same business object. Ask how deduplication keys are scoped and retained, and which semantic duplicates remain your responsibility.
Next, send an update after a later update has already arrived. Ask how the application avoids regressing state. The correct design may involve object versions, timestamps with defined semantics, or fetching current state from the source. The important buying question is whether the platform exposes the information your chosen design needs.
| Sandbox exercise | Observe | Responsibility to clarify |
|---|---|---|
| Repeat one event | Attempts and business effects | Delivery deduplication versus application idempotency |
| Reverse two updates | Final object state | Ordering guarantees and conflict handling |
| Stop the receiver | Backlog and retry behavior | Retention and recovery limits |
| Replay an old event | Operator action and new trace | Permission and duplicate protection |
| Rotate a secret | Valid and invalid request handling | Overlap period and rollback |
Make a failure last longer than the happy-path demo
Ask the vendor to simulate receiver errors, timeouts, and rate limits separately. Record retry intervals, retry limits, retention, and the state after attempts are exhausted. A retry policy should be visible in documentation and the purchased plan, not only in a sales engineer’s temporary configuration.
Shopify’s webhook documentation discusses the need to account for delivery behavior and recover data when necessary. Use that as a reminder to ask about source reconciliation as well as message retries. If the delivery service never received an event, replaying its internal queue cannot recover that missing event.
For a hypothetical small team, a weekend outage is a useful planning scenario. Ask whether Monday’s operator can identify the affected period, export the unfinished events, and recover them without replaying unrelated successful work. Have the vendor show a bounded replay selection rather than a single button that resends everything.
Inspect verification and operator permissions
Request a demonstration of signature validation using the sender’s documented method. Stripe’s guidance specifically notes that signature verification needs the raw request body. Ask what happens if a proxy or transformation changes the body, and whether validation occurs before or after that transformation.
Review who can change destinations, view payloads, replay events, or rotate signing material. Use synthetic sensitive fields to see whether logs and exports respect the intended access controls. Ask for an audit record of destination changes and manual replays, including the operator and selection criteria.
Our API management buying guide covers adjacent gateway responsibilities. Use the workflow automation checklist when a delivery triggers several downstream actions. Neither purchase should leave ownership of duplicate business effects undefined.
Price retries, retained payloads, and departure
- Ask whether billing counts original events, delivery attempts, destinations, or a combination.
- Include retries and test traffic in a realistic usage estimate.
- Confirm retention limits for payloads, metadata, and audit records separately.
- Request an export demonstration with identifiers and timestamps intact.
- Document how destinations and secrets move when the service is replaced.
- Assign an owner for source reconciliation and exhausted-delivery alerts.
Do not assume that the cheapest entry tier supports the retention or access controls shown in the demo. Put the required features beside the actual quoted plan. If an overage or upgrade is needed for the outage scenario, make that visible before approval.
Finish the evaluation with one evidence packet: the boundary diagram, sandbox event records, observed failure behavior, plan limits, and open issues. A platform is a stronger purchase when the team can explain how to recover a single failed business event without guessing or creating another one.
Frequently asked questions
Does HTTP 200 mean the business action finished?
Not necessarily. Ask whether it acknowledges receipt, storage, or completed processing.
Can the platform guarantee exactly-once business effects?
Do not infer that from delivery marketing. Inspect application idempotency and every downstream boundary.
Should we test out-of-order events?
Yes, where the source can deliver them. Confirm that the application preserves the intended final state.
Is automatic retry enough for recovery?
No. Ask about exhausted attempts, retention expiry, missing source events, and authorized replay.
What should decide the purchase?
Documented behavior under your failure scenarios, clear responsibility boundaries, and an affordable operating and exit plan.
Primary documentation
- Stripe: webhook delivery and signature guidance
- Shopify: webhook concepts and delivery behavior
- GitHub: webhook best practices
Documentation checked September 14, 2026. Vendor examples explain integration behavior and are not product rankings or endorsements.